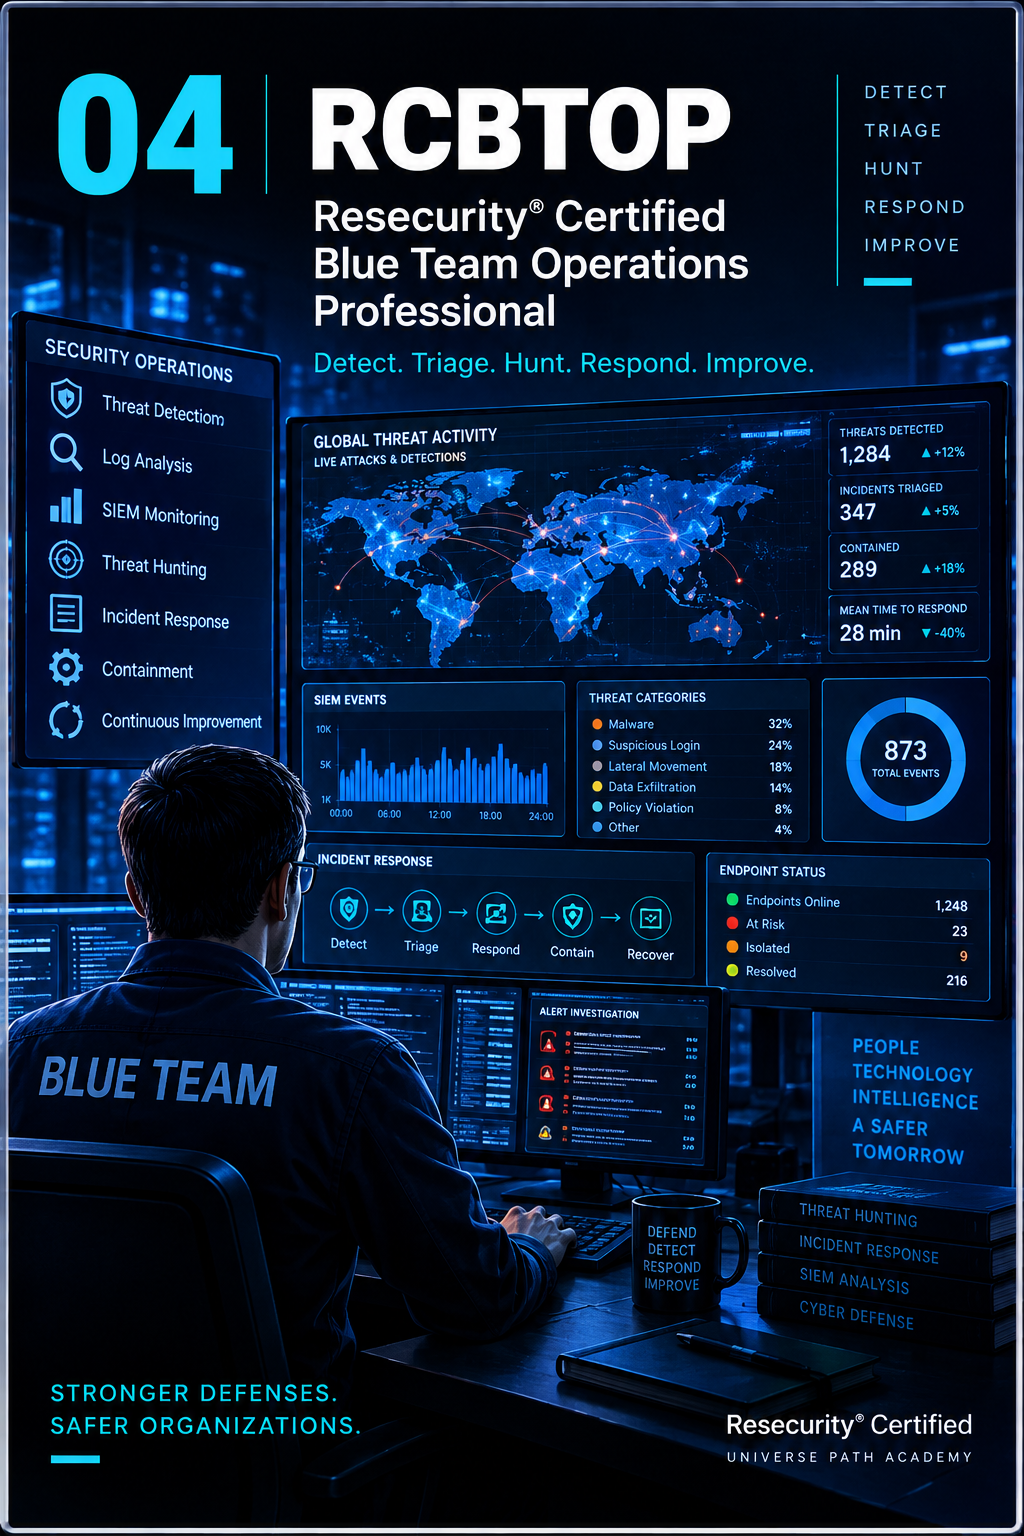
Resecurity® Certified Blue Team Operations Professional
Detect. Triage. Hunt. Respond. Improve.
A practical defensive-security programme designed to develop professionals capable of detecting, analyzing, investigating and responding to cyber threats across enterprise environments. The course follows the operational defensive cycle of Detect → Triage → Investigate → Hunt → Respond → Improve, integrating security telemetry, SIEM concepts, endpoint security, detection engineering, threat intelligence and incident response.
• Blue Team Professionals • SOC Analysts • Security Analysts • Cybersecurity Analysts • Detection Analysts • Threat Hunters • Security Monitoring Analysts • Endpoint Security Analysts • Security Operations Professionals • Incident-Response Analysts • Security Engineers • Cyber Defense Professionals
- Participants should be able to:
- • Explain the operational role of a Blue Team.
- • Analyze security telemetry, logs and alerts.
- • Perform structured alert triage and prioritization.
- • Correlate events across multiple data sources.
- • Apply SIEM concepts to defensive investigations.
- • Analyze endpoint security telemetry.
- • Develop and improve detection logic.
- • Conduct threat-hunting activities.
- • Use CTI to support defensive investigations.
- • Identify attacker behavior and attack paths.
- • Support incident containment and response.
- • Identify detection gaps and recommend defensive improvements.
Participants should have previous exposure to: • Cybersecurity fundamentals • Networking • Windows/Linux systems • Security concepts • Basic logs and alerts • Common cyber threats Equivalent academic, training or professional experience is acceptable. N9/Cybersecurity Professional Foundations is an appropriate preparation route for newcomers.