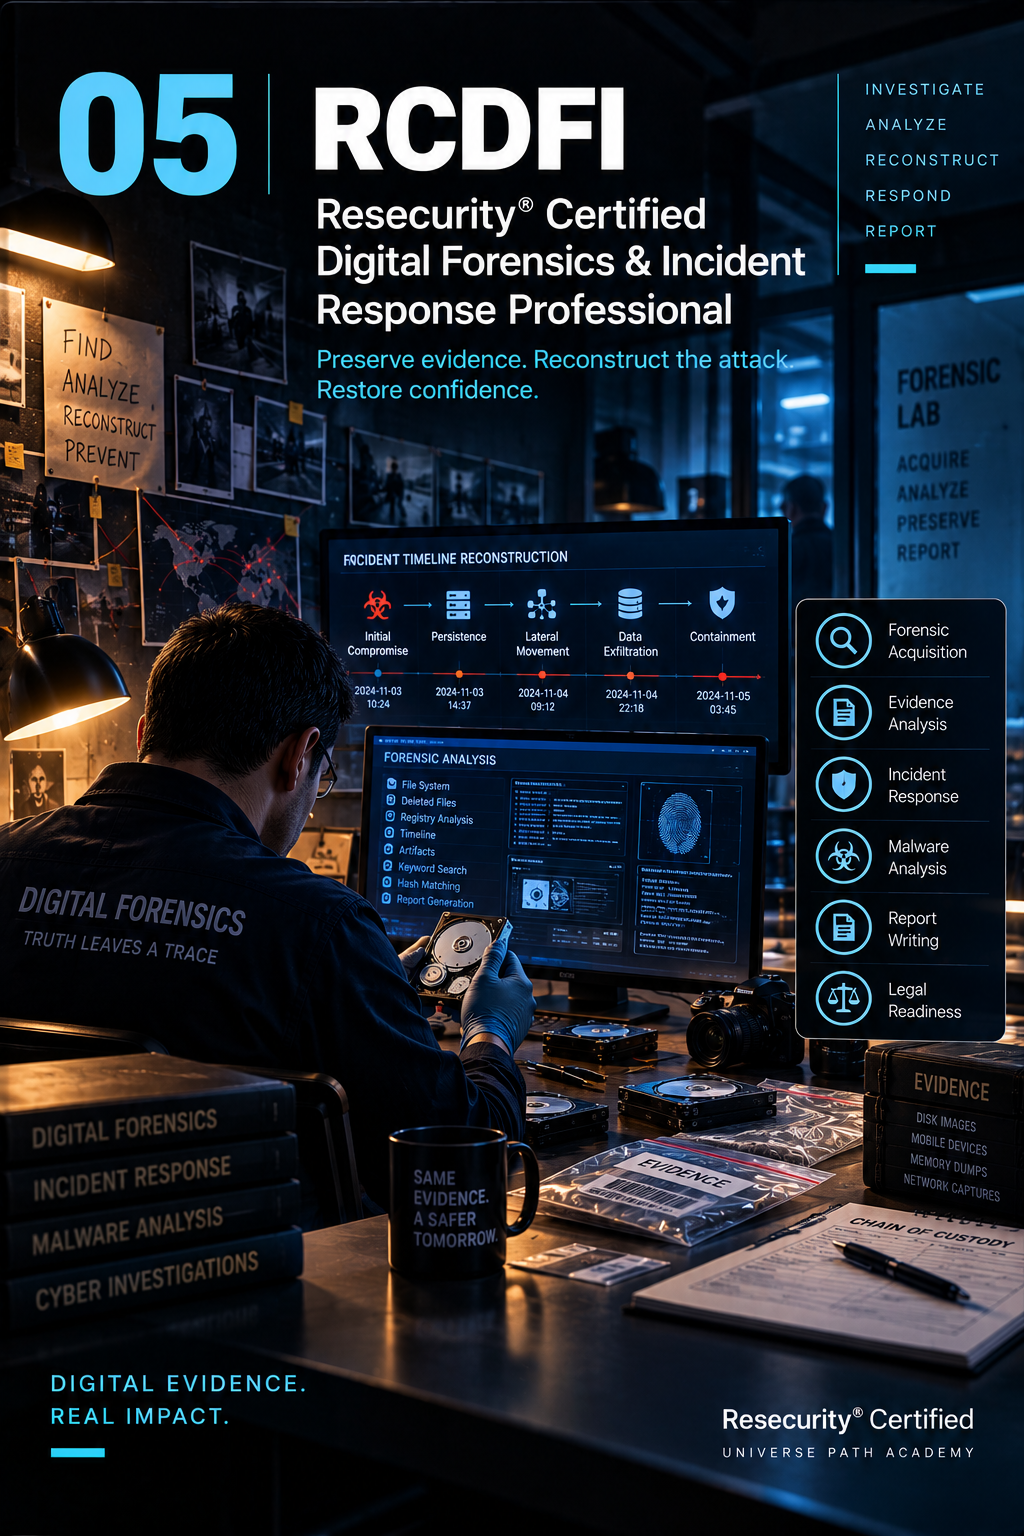
Resecurity® Certified Digital Forensics & Incident Response Professional
Preserve evidence. Reconstruct the attack. Restore confidence.
An advanced professional programme for incident responders, DFIR practitioners, SOC analysts and cybersecurity investigators with foundational knowledge or professional experience. The course develops practical capabilities in digital evidence handling, forensic acquisition, endpoint and filesystem analysis, memory forensics, network and log analysis, attacker reconstruction, incident investigation and defensible reporting. Participants investigate a realistic enterprise incident from initial triage through evidence preservation, forensic examination, attack reconstruction, impact assessment and reporting.
• Incident Responders • DFIR Analysts • SOC Analysts • Digital Forensic Examiners • Cybersecurity Investigators • Security Engineers • Threat Hunters • Senior System / Network Security Professionals • Cybersecurity professionals moving into DFIR
- Participants should be able to:
- • Conduct structured incident triage.
- • Develop evidence acquisition plans.
- • Preserve digital evidence appropriately.
- • Analyze endpoint and filesystem artifacts.
- • Conduct memory analysis.
- • Analyze network and authentication evidence.
- • Correlate multiple forensic evidence sources.
- • Reconstruct attacker activity and develop evidence-based timelines.
- • Identify persistence, lateral movement and potential exfiltration.
- • Determine root cause and identify control weaknesses.
- • Develop remediation recommendations.
- • Produce defensible forensic reports.
- • Brief technical and executive stakeholders.
Participants should have prior academic, professional or training experience in: • Cybersecurity • Incident response • Security operations • System administration • Or a related discipline Familiarity with Windows/Linux systems, networking, security events/logs and basic incident-response concepts is recommended.