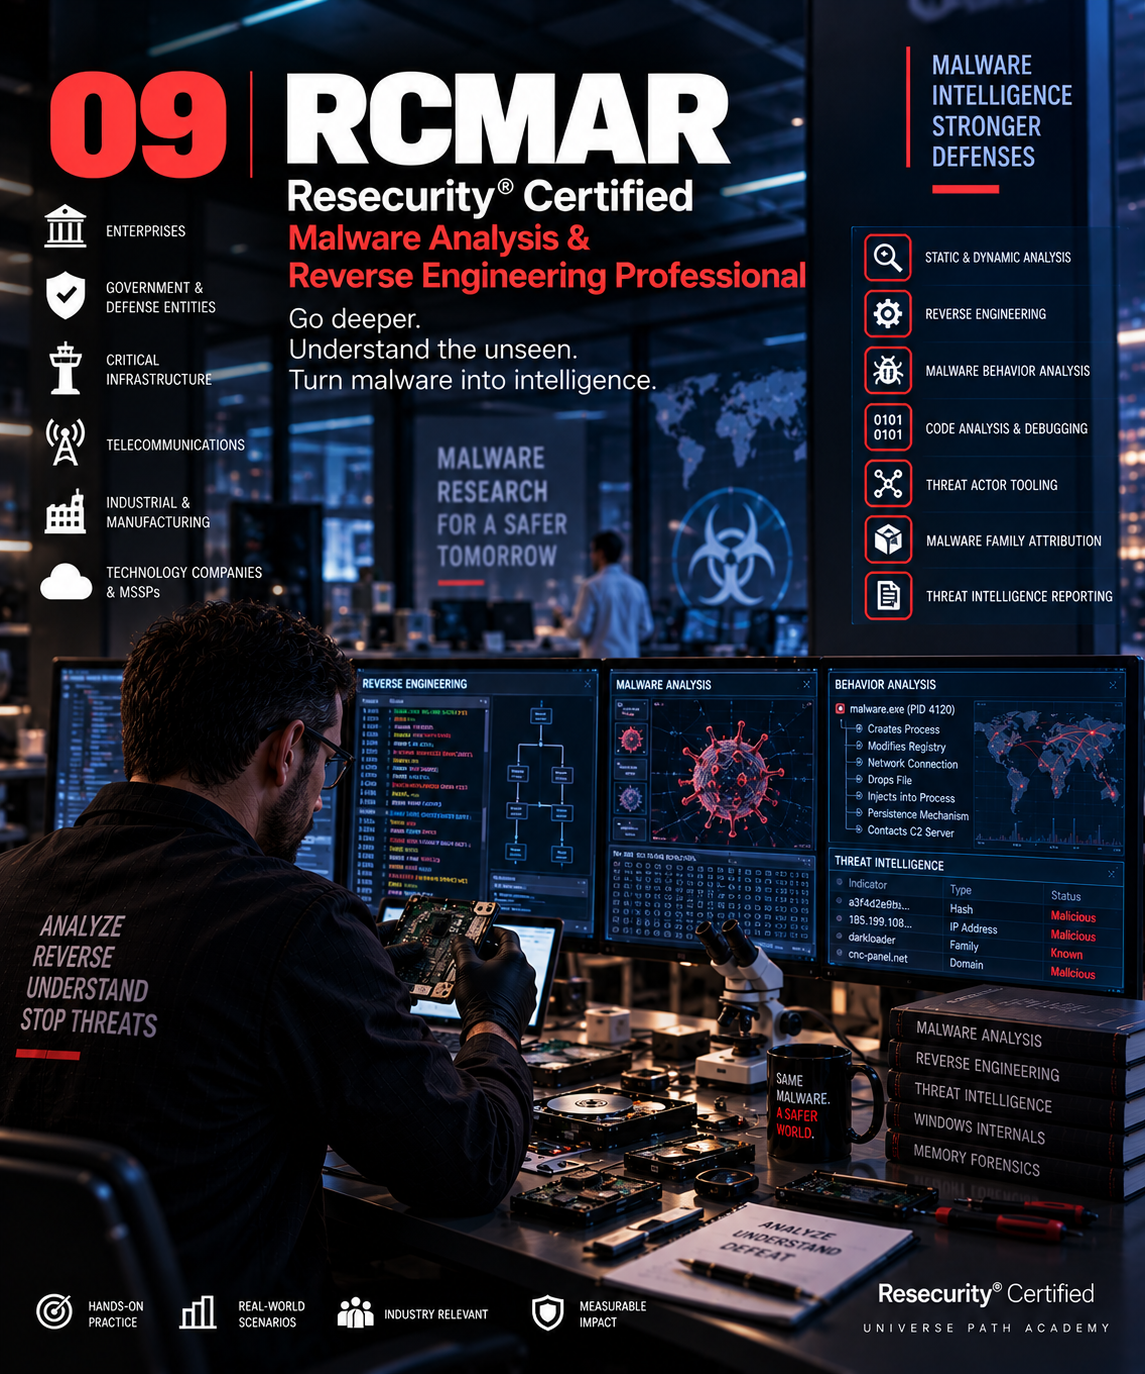
Resecurity® Certified Malware Analysis & Reverse Engineering Professional
Understand the malware. Reconstruct the behaviour. Extract intelligence.
An advanced practical programme designed to develop professionals capable of safely analyzing suspicious and malicious software, determining its behavior, extracting indicators of compromise, identifying persistence and command-and-control mechanisms, and performing introductory-to-intermediate reverse-engineering activities. Participants progress through static, dynamic and behavioral analysis, reverse engineering and intelligence extraction.
• Malware Analysts • Malware Researchers • Junior / Intermediate Reverse Engineers • Cybersecurity Analysts • Threat Intelligence Analysts • Threat Researchers • SOC Analysts • Incident Responders • Digital Forensics Professionals • Security Researchers • Detection Engineers • Security Engineers
- Participants should be able to:
- • Establish a safe malware-analysis environment.
- • Conduct initial malware triage.
- • Perform static and dynamic malware analysis.
- • Analyze malware behavior and execution chains.
- • Identify persistence mechanisms and command-and-control behavior.
- • Extract indicators of compromise.
- • Analyze suspicious processes and artifacts.
- • Perform introductory reverse engineering.
- • Navigate disassembled and decompiled code.
- • Trace relevant execution paths and behavioral routines.
- • Develop malware profiles.
- • Identify detection opportunities.
- • Produce professional malware-analysis reports.
Participants should already understand: • Basic cybersecurity concepts • Networking fundamentals • Windows/Linux fundamentals • Files and processes • Common security terminology • Basic command-line usage Prior SOC, CTI, incident-response, programming/scripting or security-research experience is useful but not mandatory.